WordPress Backup and Restore Testing: A Maintenance Essential
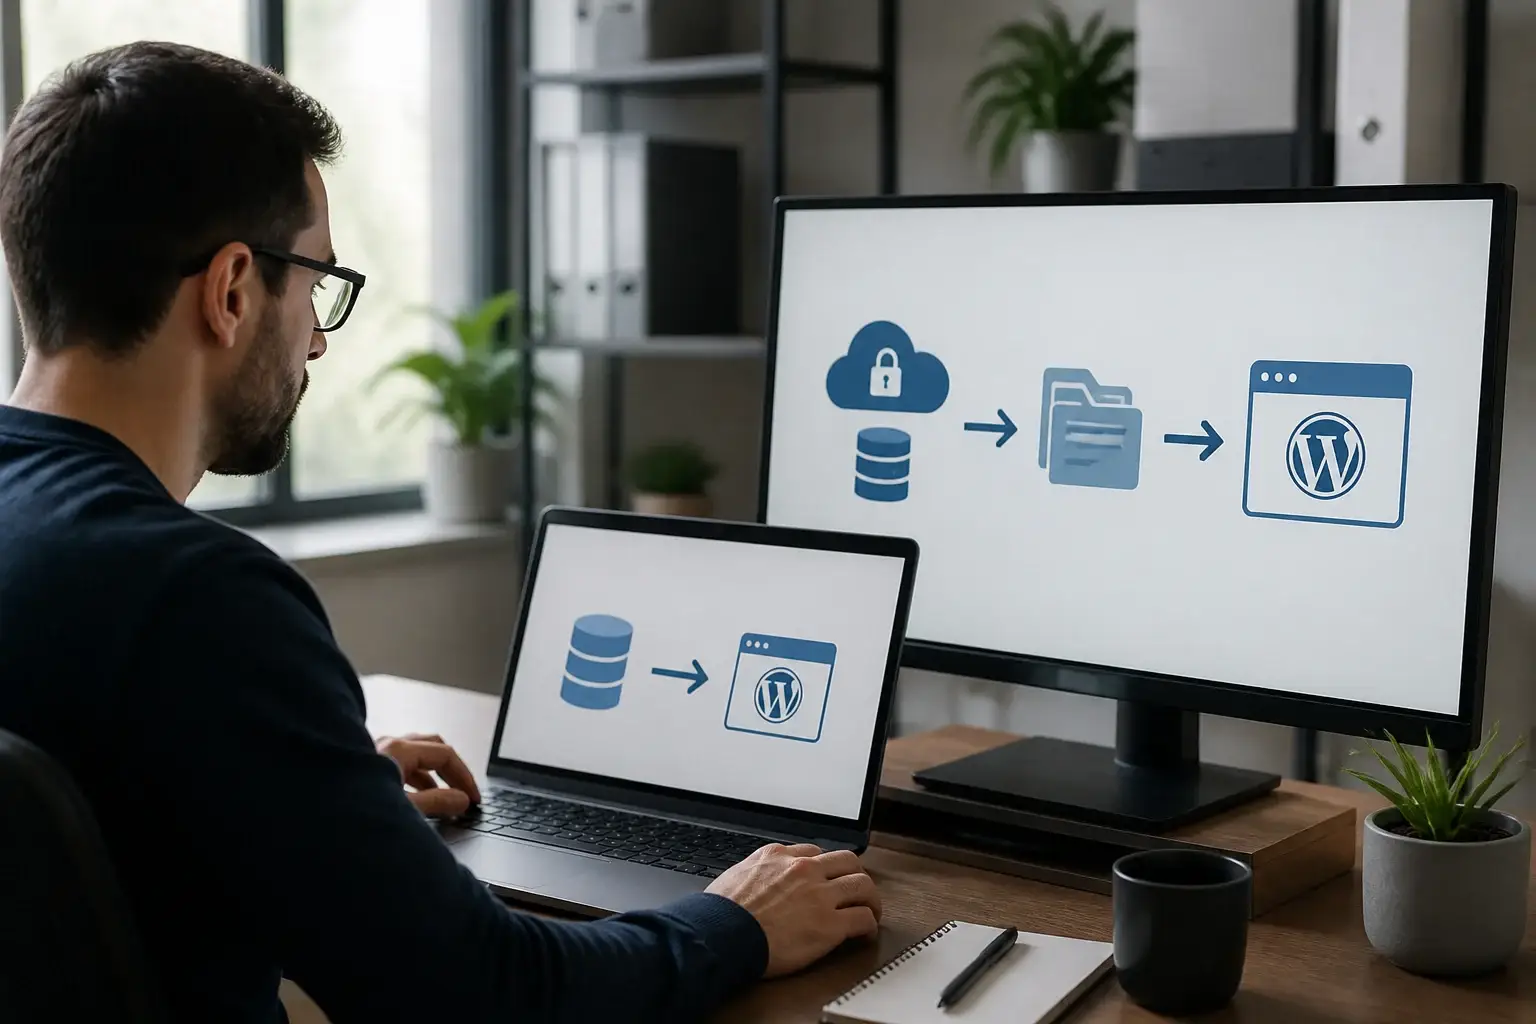
A WordPress backup is valuable only when it can restore the site you actually need. Files may appear in cloud storage, a plugin may report success, and an administrator may receive a reassuring notification, yet the archive could be incomplete, corrupted, outdated, or impossible to use on the available server. Restore testing closes that gap. It changes backup maintenance from a checkbox into a practical recovery capability.
Testing does not require taking a busy production website offline. A safer process copies backups into an isolated staging environment, confirms that the database and files work together, checks important visitor journeys, and records what succeeded or failed. Repeating this process on a defined schedule reveals problems before an outage, attack, failed update, or hosting mistake makes recovery urgent.
Why backup testing matters
A WordPress installation depends on more than the visible pages. The database contains posts, pages, settings, users, comments, menus, and many plugin records. The file system contains WordPress core files, themes, plugins, uploaded media, configuration files, and sometimes custom code. A usable recovery normally requires compatible copies of both.
A backup can fail in several ways. A database export may stop midway. Uploads may be excluded to reduce storage use. A backup may contain files from one moment and a database from another, creating mismatched content. Encryption keys, environment variables, server rules, or configuration values may be absent. A plugin may claim completion while silently skipping unreadable files. Even a complete archive can be unusable if nobody knows its password, location, format, or restoration procedure.
Testing answers practical questions:

- Does the backup open and contain expected components?
- Can it be restored on a clean, separate environment?
- Do the database and files belong to the same recovery point?
- Can administrators log in after restoration?
- Do themes, plugins, images, forms, search, and navigation work?
- How long does recovery take?
- Which person can perform it if the usual administrator is unavailable?
These answers matter because recovery decisions are made under pressure. A documented, rehearsed process reduces guessing and prevents avoidable delays.
What a complete WordPress backup includes
Before testing restoration, define the recovery scope. A full site backup generally includes the database and the WordPress file system. The database should include all tables used by WordPress and active extensions, not merely the standard core tables. Custom tables may hold ecommerce orders, membership records, bookings, or form submissions.
The file backup should include the `wp-content` directory, especially uploads, active themes, plugins, and custom code. The `wp-config.php` file contains database connection information and security salts, but copying it into an exposed location can create a serious security risk. Server configuration, PHP settings, web server rules, scheduled tasks, DNS records, external storage, and payment or email integrations may sit outside the WordPress directory. They might not belong inside every archive, but they must be documented as separate recovery dependencies.
Decide how much historical coverage the site needs. A daily backup may suit a low-change brochure site, while a store or publishing operation may need more frequent database protection. Retention should preserve enough recovery points to handle delayed discovery, accidental deletion, and unwanted changes. Do not confuse retention with testing: keeping many untested archives does not prove that any of them can restore successfully.
A useful inventory lists the backup tool, destination, encryption method, retention policy, archive format, schedule, included components, responsible owner, and restoration prerequisites. Record versions of PHP, WordPress, themes, and important plugins when practical. Version information helps recreate a compatible test environment and diagnose failures.
Build a safe testing environment
Never experiment first on the live site. Create an isolated staging installation on a separate hosting account, server, local machine, or protected temporary environment. The environment should not be publicly indexed and should not send real email, process live payments, or expose copied personal information.
Use access controls and, where appropriate, a firewall or temporary restriction. Disable outbound email or route messages to a test inbox. Replace payment credentials with sandbox credentials. Prevent search engines from indexing the restored site, but remember that a visibility setting is not a security boundary by itself. Remove or anonymize sensitive data when organizational policy requires it.
The test environment should resemble production closely enough to make results meaningful. Match the PHP version, database engine, WordPress version, web server behavior, object caching, storage limits, and required extensions as far as feasible. A less similar environment can still reveal whether an archive is structurally usable, but it may not expose compatibility problems that appear during a real emergency.
Document the staging address, access details, server resources, and cleanup procedure. If the environment is temporary, set an expiration date. Stale copies of a site create privacy and security risks, particularly when they contain customer accounts or private submissions.
A repeatable restore test
1. Select and identify the recovery point
Choose an archive according to a documented reason, such as the most recent scheduled backup or a point before a known change. Record its timestamp, source, size, checksum if available, and storage location. Confirm that the archive was transferred completely and that required decryption credentials are accessible through an approved password-management process.
Do not alter the only copy while inspecting it. Work from a duplicate when the tool or storage system permits. Preserve the original metadata so later investigation can distinguish the source archive from extracted test files.
2. Restore the database
Create an empty test database with appropriate credentials, then import the backup using the documented method. Large databases may require command-line tools, adjusted upload limits, or a staged import. Watch for timeout messages, truncated output, encoding errors, missing tables, and permission failures.
After import, confirm that expected tables exist and that row content is plausible. Check recent posts, pages, users, settings, orders, and other business records. A successful import command alone is not sufficient; a database can load while important tables are absent or damaged.
Update the test site’s database connection settings, then replace production URLs with the staging address using a method that respects serialized data. Blind text replacement can corrupt serialized values. Use a WordPress-aware migration method or a carefully chosen command-line tool, and take special care with media URLs, redirects, and multisite configurations.
3. Restore the files
Extract the file archive into the test document root or use the backup system’s restoration workflow. Confirm that uploads exist, plugin and theme directories are present, and custom files have the expected permissions. Check that the WordPress configuration points to the test database and that secrets are handled safely.
Do not assume the newest files and newest database belong together. If the backup system creates separate components, use matching timestamps or the vendor’s coordinated restore process. Mixing recovery points can produce missing media, references to nonexistent products, or inconsistent settings.
4. Repair environment-specific settings
A restored site may retain production paths, domain names, cron schedules, caching configuration, or email services. Adjust these deliberately rather than changing everything indiscriminately. Clear page caches and object caches, regenerate rewrite rules, and verify file permissions according to the hosting platform’s normal security model.
Avoid running routine updates during the first restoration test. The purpose is to evaluate the backup, not to introduce a second variable. Once the baseline works, a separate exercise can test upgrading the recovered site.
Verify what visitors and administrators need
Begin with a technical smoke test. Open the homepage, several representative posts or pages, archives, menus, search, category pages, and media files. Test both desktop and mobile layouts when the site relies on responsive behavior. Inspect browser errors, broken images, redirect loops, missing stylesheets, and unexpectedly slow requests.
Log in with a test administrator account and confirm that the dashboard loads. Check editing, media uploads, plugin settings, theme customization, scheduled tasks, and user roles. If the site uses membership or ecommerce functions, test representative workflows without sending real messages or charging real accounts.
Forms deserve focused attention. Submit contact, registration, newsletter, booking, or support forms using test information. Confirm validation, database storage, notifications, spam controls, and any connected service. Verify that payment gateways, analytics, search integrations, maps, and social publishing use sandbox or disabled credentials. A site that displays pages but cannot capture a lead or complete an order is not fully restored.
Compare the restored site with production using a checklist. Check the latest content, media, navigation, settings, user accounts, custom post types, taxonomies, and critical integrations. Record each test as passed, failed, blocked, or not applicable. Screenshots, timestamps, and error logs provide useful evidence, particularly when several people share responsibility.
Measure recovery performance
A restoration test should measure more than correctness. Record the time required to locate credentials, download the archive, provision the environment, restore the database, extract files, configure the site, and complete verification. This produces a practical recovery time estimate rather than an optimistic assumption.
Also estimate how much recent data would be lost if the latest usable backup were restored. This recovery point objective depends on backup frequency, completion reliability, and the time at which failures are detected. Recovery time objective describes how quickly the site must return to service. These are operational targets, not promises, and they should reflect business consequences.
For example, a portfolio site may tolerate a longer outage and some lost updates, while a store may need frequent database protection and a carefully rehearsed failover plan. The correct design depends on revenue, regulatory obligations, customer expectations, staffing, and the cost of downtime.
If restoration is too slow, improve the process rather than merely buying more storage. Pre-document commands, maintain a compatible staging template, keep credentials accessible, use efficient transfer methods, and clarify who approves DNS or hosting changes. Faster recovery comes from removing uncertainty as well as reducing technical duration.
Common failures and corrective actions
The archive is incomplete
Missing uploads often indicate an exclusion rule, interrupted transfer, permission problem, or insufficient storage. Review backup logs, compare file counts or selected directories, and test a new archive. Do not simply mark the task complete because the database restored.
The database imports with errors
Large imports can exceed limits or encounter incompatible character sets. Use an appropriate import method, examine the first and last lines of the dump, and verify table completeness. If errors recur, obtain assistance from the host or backup-tool documentation rather than ignoring warnings.
The site shows a blank page or fatal error
The restored environment may use an unsupported PHP version, missing extension, incompatible plugin, exhausted memory, or damaged file. Enable safe diagnostic logging without displaying sensitive errors publicly. Disable plugins methodically in the isolated environment, identify the failing component, and document the compatibility requirement. Do not treat disabling a plugin as a complete solution if the live site depends on it.
URLs, redirects, or media are broken
Production URLs may remain in database settings, serialized options, cached files, or content. Use a safe search-and-replace method, clear caches, regenerate permalinks, and inspect redirect rules. Test both secure and nonsecure requests only within the protected environment.
Email or integrations behave dangerously
Copied credentials can send messages, create records, charge accounts, or trigger external automation. Before testing, disable outbound services or replace credentials with test versions. Include this safeguard in the written procedure, not only in someone’s memory.
Schedule and document testing
Test every new backup process before trusting it, after major changes to hosting or backup tools, and periodically thereafter. The appropriate interval depends on site risk and change frequency. High-value or frequently changing sites benefit from more frequent exercises; low-risk sites should still avoid leaving restoration untested for long periods.
Use a short runbook with numbered actions, responsible roles, locations, credentials process, expected results, rollback steps, and escalation contacts. Store it separately from the production server and backup destination. If both the site and its instructions disappear together, the runbook cannot help.
After each exercise, hold a brief review. Identify failed checks, unclear instructions, excessive duration, missing access, and security concerns. Assign an owner and deadline for each correction, then retest the changed component. A test that exposes a problem is successful in one important sense: it reveals the weakness while recovery is still optional.
Protect archives throughout the lifecycle. Use reputable storage, access controls, encryption where appropriate, separate credentials, and more than one location. Keep at least one recovery option independent of the production host. Monitor backup jobs and storage capacity, and ensure alerts reach someone who can act. Security, availability, and recoverability must be considered together; an unencrypted public archive is not an acceptable solution merely because it restores quickly.
Frequently asked questions
Is a successful backup notification enough?
No. A notification usually confirms that a job completed according to the tool’s internal checks. It does not prove that every required file was included, that the database is coherent, or that the archive can be restored in a usable environment. Restoration testing provides that evidence.
Can I test by restoring over the live site?
Avoid it. A mistake can destroy current content, interrupt visitors, expose test data, or trigger real integrations. Use an isolated environment. If a production restoration is unavoidable during a genuine emergency, preserve the current state first and follow an approved change procedure.
Should I test every backup?
Testing every archive may be impractical, but every backup system and major configuration change should be tested. Periodic sampling, including different dates and storage locations, can reveal whether the process remains reliable. For critical sites, more frequent or automated validation may be justified.
What if staging cannot match production?
Test as closely as resources allow, then document differences. A structurally valid restore in a different environment is useful, but it cannot guarantee compatibility with production. Prioritize matching PHP, database, extensions, web server behavior, storage, and caching where those factors affect the site.
Do backups need to include plugins?
Usually, yes, if the goal is a complete site restoration. Plugins may contain essential code, settings, custom database tables, or integration logic. You should still maintain a list of plugin versions and licenses, because an archive may not replace access to external services or update credentials.
How long should a restore test take?
There is no universal correct duration. Measure your actual process and compare it with business requirements. The result should include preparation, restoration, configuration, verification, and any DNS or hosting work needed for a real incident. If the measured duration is unacceptable, improve the runbook and infrastructure.
Is a staging copy a backup?
No. Staging is another working copy and can become outdated, corrupted, exposed, or accidentally altered. It may support testing, but it should not replace independent, protected backups with suitable retention.
Conclusion
WordPress backup maintenance is incomplete until restoration has been demonstrated. A dependable program protects both database and files, stores copies securely, preserves appropriate recovery points, and documents dependencies beyond the WordPress directory. More importantly, it repeatedly proves that an archive can become a functioning site.
Create an isolated test environment, restore a known recovery point, inspect database and files, verify real visitor and administrator workflows, measure recovery time, and record every defect. Repeat after meaningful changes and on a schedule suited to the site’s risk. This discipline turns reassuring backup reports into credible resilience. When an incident occurs, preparation cannot remove every problem, but it can replace improvisation with a tested path back to service.